◈
Data control
Keep data handling aligned to your operating requirements and agreed source workflows.
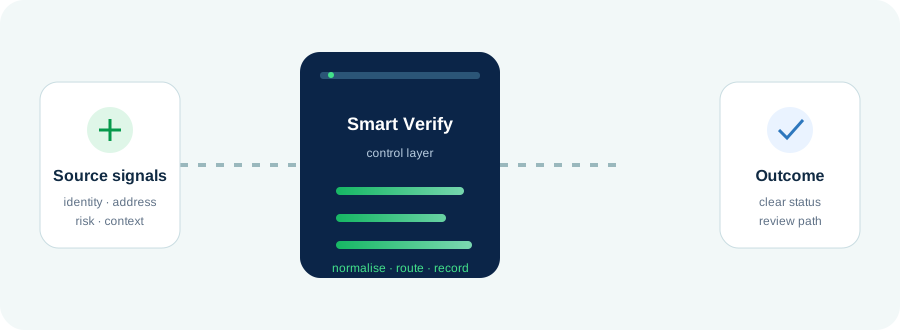
Smart Verify is built to make control, data boundaries and review behaviour visible to the teams responsible for them.
We keep our public promise precise: local operating context, controlled access and auditable workflows. Specific implementation details are covered during onboarding and technical review.
Keep data handling aligned to your operating requirements and agreed source workflows.
Make request state, outcome and review hand-offs easier to understand and investigate.
Bring the right people into the right workflow with role-aware operational controls.
We would rather scope security accurately than hide behind generic claims. Ask us about data flows, environments, retention, access, incident response and integration boundaries.
Start a security review ↗Good security language should help a buyer ask better questions. SmartVerify makes the boundaries visible: what enters the workflow, who can act, what is recorded and what happens when a source is uncertain.
Requests should carry a declared lawful purpose and an authorised operator or system context. Consent is required where the selected journey depends on it.
Use the smallest subject and document set needed for the chosen workflow. Do not place identity numbers, passwords or API keys into general enquiries.
Record request state, service code, provider response handling, review decisions and the next action so an outcome can be investigated later.
Timeouts, malformed responses, provider failures and incomplete results remain review states. The system does not silently retry or convert uncertainty into a pass.
POPIA compliance is not a badge applied after launch. It requires a defined purpose, appropriate authority, transparency to the data subject, access discipline, retention decisions and a way to handle data-subject requests.
Our POPIA notice explains the SmartVerify website and service-processing boundaries. Customer organisations remain responsible for their own lawful basis, notices, operator permissions and retention decisions.
Read the POPIA notice ↗